Visa has released an update to its open-source Visa Vulnerability Agentic Harness (VVAH) that extends the framework from vulnerability discovery into remediation and validation workflows.
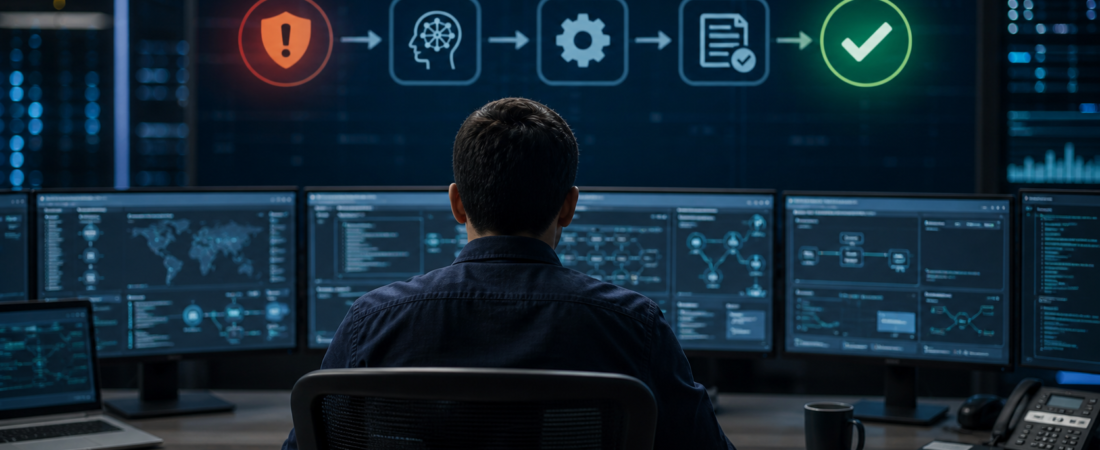
The model-agnostic framework is intended to help security teams discover, triage, remediate and validate vulnerabilities through one structured process. Visa said the update adds closed-loop remediation: when a proposed fix does not pass validation, structured feedback can be used to refine it without restarting the workflow.
The release also adds configuration-based model selection. Organizations can use approved Anthropic or OpenAI models, as well as other models through configuration changes rather than code changes, according to Visa. Optional real-time progress views are intended to give teams more visibility into longer scans and remediation work.
VVAH was initially released after Visa participated in Anthropic’s Project Glasswing cybersecurity initiative. Visa said the framework had previously been used to find vulnerabilities, assess exploitability and produce structured findings. The new release makes remediation and its validation part of that flow.
For security operations teams, the change addresses a recurring gap between identifying an exposure and confirming that a correction works. Visa said some attack-path resolution times have fallen from weeks to hours, although the company did not provide implementation details or independent performance data for that claim.
Alongside the software update, Visa Consulting & Analytics introduced three advisory offerings: AI cyber-leadership education, a VVAH-informed cybersecurity maturity assessment, and a cyber-risk prioritization and roadmap service. The services are aimed at helping organizations assess risk and sequence remediation efforts.
Visa released VVAH as open source in June 2026 and said the project has since been downloaded by tens of thousands of developers. The framework is available through Visa’s GitHub repository.